


Watch ThreatWise TV: Explorations within the spam folder
The spam folder: that darkish and disregarded nook of each electronic mail account, stuffed with too-good-to-be-true provides, sudden shipments, and supposedly free giveaways.
You’re proper to disregard this folder; few good issues come from exploring it. However each now and again certainly one of these deceptive, and typically malicious, emails manages to evade the filters that usually siphon them off, touchdown them in your inbox as a substitute.
Luckily, it’s simple sufficient to identify these emails if what to search for. We’ve investigated this folder as soon as earlier than, showcasing quite a lot of scams. With the vacation season in full swing, we thought this might be an excellent time to revisit how scammers try to trick unsuspecting customers.
The vacation season is historically a time when this kind of exercise will increase, and this 12 months is not any completely different. In accordance with analysis printed by credit score reporting company TransUnion, the typical every day variety of suspected digital fraud makes an attempt was up 82 % globally between Thanksgiving and Cyber Monday (Nov 24–Nov 28) in comparison with the remainder of the 12 months (Jan 1–Nov 23) and 127 % greater for transactions originating within the US.
This degree of exercise makes it all of the extra necessary to concentrate on these scams. With that in thoughts, let’s dive into the spam folder to get an image of the sorts of campaigns presently circulating.
A phrase of warning
Whereas a lot of the spam circulating is innocuous, many emails are phishing makes an attempt, and a few are certainly malicious. To discover these scams, we used a devoted laptop, segmented from the remainder of the community, and leveraged Cisco Safe Malware Analytics to securely open the emails earlier than clicking on hyperlinks or opening attachments. The purpose being, we don’t suggest doing this at residence.
10 questions for a tremendous reward
By far, the most important class of spam we noticed have been surveys scams. In accordance with these emails, for those who fill out a easy survey you’ll obtain “unique provides” equivalent to reward playing cards, smartphones, good watches, energy drills, and even pots and pans.

There are even some campaigns that particularly goal the vacation buying season.

Clicking the hyperlinks in these emails takes the recipient to websites the place they’re requested to fill out a survey.

These pages usually embody faux testimonials that say how simple the survey is and what they did with their free reward.

The surveys are simple, comprising 10-20 easy questions that cowl demographic data and buying habits.

After the survey is accomplished, these websites provide the selection of a handful of rewards. All of the recipient should do is pay for transport. They’re then delivered to a web page the place they will fill out transport and fee data, and the reward is supposedly shipped.

Nevertheless, the makes an attempt to make fee usually seem to fail, or the recipient is knowledgeable that the prize is now not obtainable.

An unsuspecting consumer might merely surrender at this level, disenchanted that they received’t be getting their free reward. What they might not be conscious of, is that they’ve simply given their bank card particulars away in a phishing rip-off.
Of their 2021 Web Crime Report, the Web Crime Grievance Middle (IC3) stated that Non-Fee / Non-Supply scams equivalent to these led to greater than $337 million in losses, up from $265 million in 2020. Bank card fraud amounted to $172 million in 2021 and has been climbing constantly at a conservative charge of 15-20 % since 2019.
In accordance with Cisco Umbrella, most of the websites asking for bank card particulars are identified phishing websites, or worse, host malware.

Your package deal is in route
One other matter that we coated the final time we explored a majority of these scams was package deal supply spam. These proceed to flow into right this moment. There are a selection of transport corporations impersonated in these campaigns, and a few generic ones as properly.

Many of those campaigns declare {that a} package deal couldn’t be delivered. If the recipient clicks on a hyperlink in an electronic mail, they’re delivered to an internet web page that explains that there are excellent supply charges that must be paid.

The recipient is additional enticed by options that the package deal incorporates a big-ticket merchandise, equivalent to an iPhone or iPad Professional. All of the recipient is required to do is enter their bank card particulars to cowl the transport.

Whereas no outright malicious exercise was detected whereas analyzing these emails in Safe Malware Analytics, a number of suspicious behaviors have been flagged. Likelihood is the dangerous actors behind these campaigns are phishing for bank card particulars.

Plain-text messages
Typically the best approaches can work simply in addition to the flashiest. This definitely holds true with spam campaigns, given the prominence of plain-text messages.

The subjects coated in such emails run the gamut, together with medical cures, 419 scams, romance and courting, prescription drugs, weight reduction, and most of the rip-off sorts we’ve already coated. Many of those hyperlink to phishing websites, although some try to determine a dialog with the recipient, tricking them into sending the scammers cash.
The IC3 report says that victims of confidence fraud and romance scams misplaced $956 million collectively, which is up from $600 million in 2020. Healthcare fraud, such because the miracle capsules and prescriptions scams, resulted in $7 million in losses in 2021, however almost $30 million in 2020. Whereas a majority of these scams appear generic and simply noticed, they nonetheless work, and so it’s necessary to bear in mind and keep away from them.
Issues together with your account
Many emails hitting the spam field try and trick customers of varied providers into believing that there’s a drawback with their account. The issues cowl all types of providers, together with streaming platforms, electronic mail suppliers, antivirus subscriptions, and even public data.

If the hyperlinks are clicked, the recipient is offered with touchdown pages that mimic the respective providers. Any particulars which are entered will possible be phished, resulting in account takeover and/or entry to non-public data. Nevertheless, some domains encountered in these instances might do extra than simply steal data, they might ship malware too.

Billing scams
One other ceaselessly encountered rip-off surrounds billing. Many of those look like sudden payments for providers the recipient by no means bought.
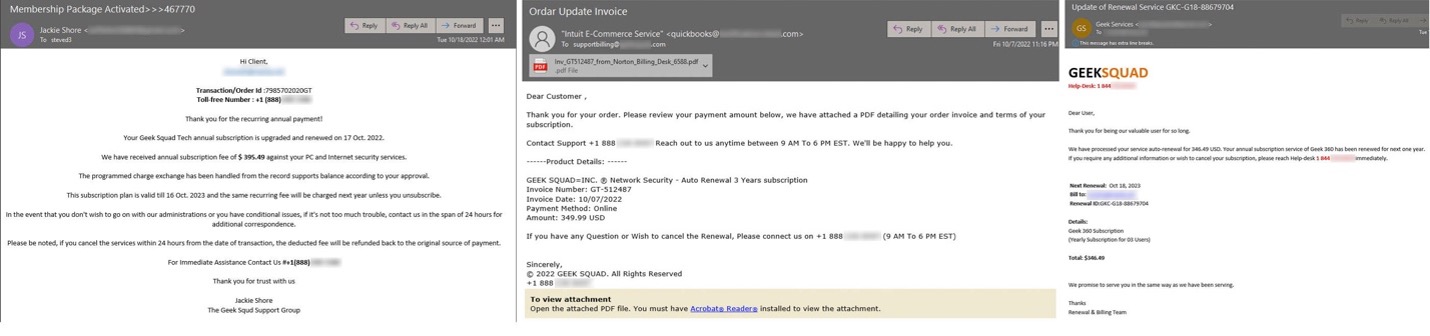
These emails embody attachments which are designed to appear to be official invoices. Curiously, a lot of the attachments that we appeared presently have been innocent. The objective is to get the recipient to name what seems to be a toll-free quantity.

Whereas we haven’t known as any of those numbers, the expertise normally unfolds like a normal customer support name. In the long run the “brokers” merely declare the fees—which by no means existed within the first place—have been eliminated. In the meantime the scammers steal any private or monetary data offered in the course of the name.
Malicious billing scams
Whereas most billing scams we encountered performed out as described above, a number of did certainly include malware.
On this instance, the e-mail seems to come back from an web service supplier, informing us that our month-to-month invoice is prepared.

An bill seems to be connected, saved inside a .zip file. If the recipient opens it and double clicks the file inside, a command immediate seems.

This may occasionally appear uncommon to the recipient, particularly since no bill seems, however by this level it’s too late. The file incorporates a script that launches PowerShell and makes an attempt to obtain a distant file.

Whereas the distant file was now not obtainable on the time of study, there’s a excessive probability it was malicious. However though we have been unable to find out its contents, Safe Malware Analytics flagged the script execution as malicious.

Defending your self
Realizing about prevalent scams, particularly in the course of the vacation season, is a primary step in guarding towards them. Granted the dangerous actors who distribute these spam campaigns do all the things they will to make their scams look reliable.
Luckily, there are a number of issues that you are able to do to establish scams and defend towards them:
- Be cautious of any unsolicited provides, giveaways, and different suspicious communications.
- Be certain that the sender’s electronic mail deal with corresponds with the group it claims to come back from. In most of the examples above they don’t.
- When vacation buying, stick with identified distributors, visiting their web sites instantly or utilizing their official apps.
- Don’t open hyperlinks or attachments in emails coming from unknown sources.
However even one of the best of us may be fooled, and when overseeing a big operation it’s extra a matter of when, slightly than if, somebody clicks on the flawed hyperlink. There are components of the Cisco Safe portfolio that may assist for when the inevitable occurs.
Cisco Safe Malware Analytics is the malware evaluation and malware menace intelligence engine behind all merchandise throughout the Cisco Safety Structure. The system delivers enhanced, in-depth, superior malware evaluation and context-rich intelligence to assist higher perceive and battle malware inside your environments. Safe Malware Analytics is accessible as a standalone answer, as a element in different Cisco Safety options, and thru software-as-a-service (SaaS) within the cloud, on-premises, and hybrid supply fashions.
Cisco Safe E mail protects towards fraudulent senders, malware, phishing hyperlinks, and spam. Its superior menace detection capabilities can uncover identified, rising, and focused threats. As well as, it defends towards phishing by utilizing advance machine studying methods, actual time conduct analytics, relationship modeling, and telemetry that protects towards identification deception–based mostly threats.
Cisco Umbrella unifies a number of safety capabilities in a single cloud service to safe web entry. By imposing safety on the DNS layer, Umbrella blocks requests to malware earlier than a connection is even established—earlier than they attain your community or endpoints. As well as, the safe net gateway logs and inspects all net visitors for better transparency, management, and safety, whereas the cloud-delivered firewall helps to dam undesirable visitors.
Cisco Safe Endpoint is a single-agent answer that gives complete safety, detection, response, and consumer entry protection to defend towards threats to your endpoints. The SecureX platform is constructed into Safe Endpoint, as are Prolonged Detection and Response (XDR) capabilities. With the introduction of Cisco Safe MDR for Endpoint, we’ve mixed Safe Endpoint’s superior capabilities with safety operations to create a complete endpoint safety answer that dramatically decreases the imply time to detect and reply to threats whereas providing the best degree of always-on endpoint safety.

We’d love to listen to what you suppose. Ask a Query, Remark Beneath, and Keep Related with Cisco Safe on social!
Cisco Safe Social Channels
Share:

